There is a point where exposed services stop feeling like cool infrastructure and start feeling like neighbors you no longer want in the main house.
A reverse proxy.
A public dashboard.
A Git forge.
Maybe a photo service.
Maybe an experimental app you need reachable from outside for a while.
None of these are automatically evil.
But they do change the trust conversation.
And in Proxmox, I think the mistake many people make is believing a DMZ exists the moment they create another subnet or another bridge.
It does not.
An isolated DMZ is not just a different address range.
It is a decision about how traffic is allowed to cross boundaries.
- Why a virtual DMZ matters even in a small homelab
- What Proxmox officially gives you to build one
- How routed versus NATed design changes the feel of the DMZ
- Why forward rules matter more than labels
- What I would actually place inside a homelab DMZ and what I would not
A DMZ becomes useful the moment trust boundaries stop being theoretical
In a small homelab, people often delay segmentation because everything still feels personally controlled.
But the moment a service is intentionally exposed, or even just has a higher probability of being probed, updated often, or configured quickly under pressure, its relationship to the rest of the lab changes.
That is where a DMZ earns its place.
Not because you are trying to imitate enterprise architecture for fun, but because some workloads deserve a smaller blast radius.
I think that is the right way to understand it:
- not prestige segmentation;
- not “more subnets because VLANs are exciting”;
- but smaller consequences when something exposed behaves badly.
Proxmox already gives you the building blocks
The official Proxmox documentation gives you the pieces quite clearly, even if it does not hand you one giant “click here for DMZ” button.
The network-configuration docs cover Linux bridges, routed configurations, masquerading with iptables, and VLAN 802.1Q. The firewall docs explain that Proxmox groups traffic into directions and zones, including In, Out, and especially Forward, which is the piece that matters when traffic is passing between segments. The SDN docs add more advanced constructs like zones, VNets, subnets, and SNAT when you want a more abstracted virtual-network model.
That means Proxmox already gives you at least two reasonable homelab paths:
- a classic bridge/VLAN/firewall design;
- an SDN/VNet-based design if you want something more structured and scalable.
For most homelabs, I think the first path is enough.
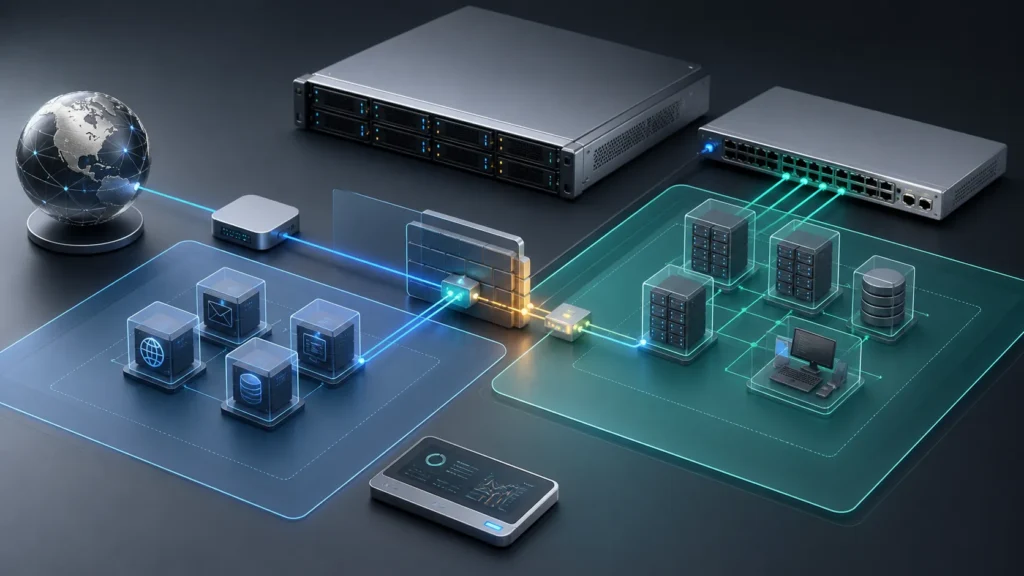
A virtual DMZ usually starts as its own bridge or VLAN-backed segment
The simplest useful pattern is easy to describe:
- create a separate virtual network segment for exposed services;
- attach only the intended VMs or containers to it;
- decide how that segment reaches the internet;
- explicitly restrict how it can reach trusted internal networks.
That segment can exist as:
- its own Linux bridge;
- a VLAN-backed bridge;
- or a VNet if you are using Proxmox SDN.
The exact implementation matters less than the intent.
What matters is that the DMZ stops sharing trust by default with storage, management, and private service networks.
If an exposed reverse proxy sits on the same casually trusted segment as your backup server, admin workstation paths, and internal databases, then calling one of those guests “DMZ” is mostly decorative.
Routed versus NATed changes the operational feel of the DMZ
The official Proxmox network docs cover both routed configuration and masquerading.
That is important because a homelab DMZ can be made to feel very different depending on which model you choose.
A routed DMZ feels cleaner when you want the segment to be a real first-class network in your design. It is easier to reason about, easier to document, and often more satisfying if you already control upstream routing or firewall policy well.
A NATed DMZ is often simpler when you mainly want isolated private addressing with controlled outbound access and carefully selected inbound forwards.
Neither is automatically superior.
The better question is:
“Do I want this segment to behave like a properly routed internal zone, or do I mainly want it to sit behind a constrained translation boundary?”
In a small homelab, NAT is often enough.
In a more deliberate segmented design, routed can feel cleaner.
Forward traffic is where the DMZ becomes real
This is the single most important point in the article.
The Proxmox firewall documentation explains Forward traffic as traffic passing through a zone. At the host level, that includes routed traffic and at the VNet level it affects traffic passing by a VNet, including bridged interfaces.
That means the real isolation question is not:
“Did I create vmbr5 and name it DMZ?”
It is:
“What forward traffic is allowed from that zone to anywhere else?”
This is why I think labels can become dangerously comforting.
A DMZ is real only when forward behavior is intentionally constrained:
- exposed services should not casually reach management networks;
- east-west trust toward private application tiers should be minimal;
- only the traffic that has a reason to exist should be permitted.
That is what shrinks the blast radius.
Without that, the segment is mostly aesthetic.
SDN and VNets are worth knowing about, even if you keep the first DMZ simple
Proxmox’s SDN documentation shows that the platform can model virtual networks more formally through zones, VNets, subnets, aliases, DHCP options, and SNAT-capable designs.
I would not tell every homelabber to begin there.
But I do think it is worth understanding that if your lab grows, Proxmox can support a more explicit virtual-network architecture without forcing you to keep everything as hand-managed bridge fragments forever.
So my view is:
- start with bridges, VLANs, and firewall clarity if that is enough;
- keep SDN/VNet in mind if segmentation is multiplying or getting hard to reason about.
That feels like a healthy progression instead of premature complexity.
What belongs in the DMZ and what usually does not
For me, the DMZ is for services whose exposure profile is different from the rest of the lab.
That usually includes things like:
- reverse proxies;
- public-facing dashboards or status endpoints;
- Git forges meant to be reachable externally;
- web applications that really do need internet-facing access.
What I usually would not place there:
- management interfaces for the hypervisor itself;
- backup infrastructure;
- internal databases unless absolutely necessary;
- storage systems that have no reason to live near exposed edges;
- identity systems unless their placement is carefully thought through.
This is where a lot of self-inflicted pain can be avoided. A DMZ is not a place for “important things.” It is a place for “things whose exposure profile is different.”
So how would I build the first version?
If I were doing this in a homelab today, I would start simply:
- create a dedicated bridge or VLAN-backed bridge for exposed services;
- place only the truly exposed workloads there;
- decide early whether the segment is routed or NATed;
- use Proxmox firewall rules with special attention to
Forwardbehavior; - prove that DMZ-to-LAN traffic is restricted the way I think it is;
- keep internal management, storage, and backups outside that segment.
That is already enough to make the design materially better than “public-ish things living next to everything else.”
Verification note: Commands, terminology, and support details in this guide were cross-checked against Proxmox’s network-configuration documentation.
For broader context, continue with Configuring Network Bridges in Proxmox: Single NIC vs Dual NIC Setups and Unprivileged vs Privileged LXC Containers: The Real Security Trade-Off.
Conclusion
Configuring a virtual isolated DMZ in Proxmox is not really about creating one more subnet and naming it well. It is about deciding how traffic is allowed to cross boundaries. The official Proxmox documentation already gives you the tools: bridges, VLAN-backed designs, routed or NATed networking, firewall directions including Forward, and more advanced SDN/VNet constructs if you want them. The important part is using those pieces intentionally so exposed services live in a segment with explicitly constrained relationships to the rest of the lab.
That is why I think a good homelab DMZ feels boring in the best possible way. Not dramatic, not performative, just smaller consequences when something on the edge stops deserving your trust.
FAQ
Is a separate VLAN or bridge automatically a DMZ in Proxmox?
No. It only becomes a meaningful DMZ when the traffic crossing that boundary is intentionally restricted, especially forwarded traffic toward trusted internal networks.
Should I use Proxmox SDN for my first DMZ?
Not necessarily. The official SDN features are useful, but many homelabs can build a very solid first DMZ with classic bridges, VLANs, and firewall rules. SDN becomes more attractive when the network design grows more complex.