For a long time, double NAT sounded to me like one of those networking phrases that arrives already wrapped in frustration.
People would mention it when port forwarding refused to cooperate, when a game console complained, when remote access got weird, or when a VPN setup seemed almost correct but never fully comfortable. The phrase itself made the problem sound exotic. The reality was much more ordinary.
Most of the time, double NAT begins with a setup that feels perfectly reasonable on the day you build it:
- the ISP gives you a modem-router or gateway;
- you buy your own router because you want better Wi-Fi, better control, or better security;
- you plug your router behind theirs;
- both devices remain in router mode;
- both devices perform NAT.
That is the whole drama in one sentence: the network now has two devices trying to be the edge.
Once that clicked for me, the subject stopped feeling mysterious. It became a topology problem, not a curse.
- What double NAT actually is
- Why it happens so easily in home networks
- What symptoms usually point to it
- How to confirm it without overcomplicating the diagnosis
- Which fix is best for each kind of setup
- When double NAT is merely annoying and when it becomes a real blocker
- How I think about it now when designing a calmer network
The protocol and configuration baseline below is checked against the official documentation at kb.netgear.com; the topology and risk recommendations are my practical interpretation.
Double NAT simply means traffic is being translated twice on its way out
Normal home NAT is already familiar even when people do not call it that. A router takes many private addresses inside the home and translates their outbound traffic so it can leave through one public-facing internet connection.
Double NAT means that translation happens at two different layers instead of one.
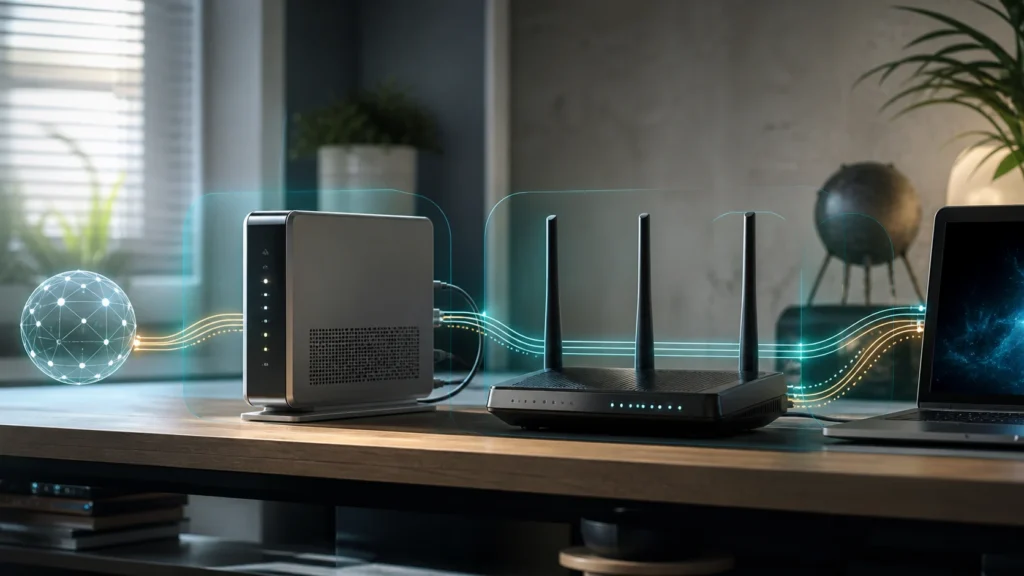
The path usually looks something like this:
- your laptop or server lives behind your own router on a private subnet;
- your router translates that traffic and sends it upstream;
- the ISP gateway receives that already-translated traffic and translates it again;
- only then does the traffic leave toward the public internet.
This is one reason I keep coming back to the basics of public and private addressing. Once you understand that NAT is a boundary behavior, double NAT becomes easier to visualize. It is not one bad packet trick. It is simply two separate boundaries stacked in the same path.
It happens because home networks often accumulate gear faster than they clarify roles
I do not think double NAT is usually caused by bad intentions. It is caused by understandable upgrades.
Maybe the ISP gateway is mediocre, so you buy a nicer router.
Maybe you add a mesh system.
Maybe you replace the default wireless with something stronger.
Maybe you move to a firewall appliance and forget the ISP box is still routing upstream.
Every one of those decisions can be perfectly sensible. The trouble begins when the older device is not demoted from router duty after the newer one arrives.
That is what makes double NAT so common. It is not advanced enough to look scary during setup, and not broken enough to fail immediately. Web browsing still works. Streaming still works. Phones still connect. So the network feels healthy right up until you ask it to do something more deliberate.
The usual signs appear when the network needs inbound clarity instead of simple outbound access
Ordinary outbound traffic often survives double NAT just fine. That is why the problem hides so well.
The symptoms usually appear when you need one of these:
- port forwarding to a self-hosted service;
- remote access into the home network;
- game console NAT behavior that wants a more direct edge path;
- peer-to-peer traffic that does not like layered translation;
- VPN setups that feel unpredictable;
- a clean mental model of which router is actually in charge.
That last symptom is not technical in the narrow sense, but I think it matters a lot. A network becomes harder to trust when the answer to "where should I configure this?" keeps changing.
If I need to forward a port, do I do it on my router, the ISP router, or both?
If I want a stable WAN identity, which device actually owns it?
If a service is unreachable from outside, which firewall surface is denying it?
Double NAT makes too many simple questions become layered questions.
Double NAT often leaves ordinary web usage untouched. The pain usually shows up only when you need inbound access, cleaner peer-to-peer behavior, or straightforward troubleshooting.
The fastest confirmation is usually checking what your own router thinks its WAN address is
The easiest test is not fancy.
Log into your own router and look at its WAN or internet-facing IP address. If that address is itself private, the network is probably sitting behind another routing layer upstream.
Common clues include WAN addresses in ranges such as:
192.168.x.x10.x.x.x172.16.x.xthrough172.31.x.x
If your router’s WAN address is private, it usually means your router is not truly on the public edge. Something in front of it is still acting like a router.
That does not always prove every form of upstream complexity, but it is one of the clearest home-network signals that you are not dealing with a single clean boundary.
Another practical check is to compare:
- the WAN IP shown in your router;
- the public IP reported by an external "what is my IP" service.
If they do not match, there is another layer involved somewhere upstream. Sometimes that is ordinary double NAT inside the home. Sometimes it can also point to carrier-grade NAT from the ISP. The important thing is that your router is not the final public-facing authority.
Option one is bridge mode on the ISP gateway, and it is usually the best answer
If you want your own router or firewall to be the true network authority, the cleanest design is usually to put the ISP gateway into bridge mode if the device and ISP support it.
That typically means:
- the ISP device stops doing the main routing and NAT job;
- your own router receives the upstream connection more directly;
- port forwarding, firewall policy, and WAN identity become centered in one place again.
This is usually the fix I would prefer when the downstream router is the device I actually trust and want to manage long term. It gives the network a single edge brain instead of two competing ones.
It also makes related services feel less confusing later, whether that is remote access, better firewall rules, or something like dynamic DNS for a changing home connection.
Option two is access point mode if the second device only needs to provide Wi-Fi or switching
Sometimes the second router does not need to be a router at all.
This is one of the most common home-network misunderstandings. A newer device may have been purchased for better wireless coverage, better hardware, or a nicer interface, but the real need may simply be stronger Wi-Fi in the same network, not a second routing boundary.
In that case, access point mode is often the better answer.
That approach keeps:
- one main router doing NAT and DHCP;
- one coherent subnet for ordinary clients;
- the second device focused on wireless coverage or simple LAN extension.
I ended up writing separately about bridge mode versus access point mode precisely because this distinction helped me stop overusing routers as if "router" were their only respectable job.
Option three is the compromise path when bridge mode is unavailable
Some ISP gateways are stubborn.
Sometimes the provider does not allow true bridge mode.
Sometimes the firmware is limited.
Sometimes a household service depends on the ISP unit staying involved in ways you do not want to break immediately.
In those cases, people often fall back to compromise approaches such as:
- putting the downstream router into the ISP router’s DMZ or exposed-host setting;
- forwarding the necessary ports through both layers;
- accepting the topology temporarily while keeping the important service expectations modest.
I do not think these are elegant fixes, but I do think they are honest ones. Not every home network can jump directly from messy to perfect.
If you do use a compromise, document it. Write down which router owns DHCP, which one owns Wi-Fi, where the WAN address lives, and where inbound rules actually exist. A surprising amount of networking stress is not caused by complexity alone. It is caused by undocumented complexity.
The problem matters most when you care about self-hosting, gaming, or clean remote access
There are environments where double NAT is mostly a nuisance and environments where it becomes a real blocker.
If all you do is browse the web, stream, and update apps, you may live with it for a long time without much pain.
If you want to:
- publish a service from home;
- reach a NAS or lab securely from outside;
- run game-related peer connections more cleanly;
- avoid doing every inbound rule twice;
- keep troubleshooting understandable;
then double NAT becomes much more expensive mentally.
That is one reason it matters so much for people building early homelabs. The moment your network stops being only a consumer network and starts becoming a place where services live, the edge architecture matters more.
The fix is often less about heroics and more about reducing authority
This may be my favorite lesson in the whole topic.
Networking gets calmer when fewer devices pretend to be the boss.
One DHCP authority is easier than two.
One NAT boundary is easier than two.
One place for port forwards is easier than two.
One firewall surface at the true edge is easier than two.
That same instinct is why I also prefer keeping device addressing readable with reservations and calmer DHCP policy instead of scattering too many assumptions across too many boxes. A network feels healthier when roles are narrow and explicit.
If your connection loads websites, that only proves outbound traffic is surviving. It does not prove the network has a single clear routing boundary or that future port-forwarding, VPN, or self-hosting tasks will be pleasant.
How I think about double NAT now
I no longer hear "double NAT" and imagine an obscure protocol problem. I hear it and ask a simpler question:
how many devices in this path still believe they are the router?
If the answer is two, the rest of the diagnosis usually becomes much easier.
Most of the time, the solution is not a clever trick. It is choosing which device should keep the edge role and then demoting the other one into a narrower, clearer job.
That shift made home networking feel much less mysterious to me. Double NAT stopped being something I feared and started being something I could spot, name, and simplify.
Conclusion
Double NAT is what happens when two routing boundaries stack on top of each other and both keep translating traffic. That design can still allow ordinary browsing, which is why it often survives unnoticed at first. The trouble begins when you need clean inbound behavior, predictable forwarding, simpler VPN logic, or a network that is easier to reason about.
What finally helped me was not memorizing more jargon. It was seeing the architecture more clearly. One device should usually be the real edge. The other should either step aside, move into bridge mode upstream, or become an access point downstream. Once the roles are honest, the network usually gets calmer very quickly.