There is a point where a single web container stops feeling tidy and starts feeling lonely.
At first, one container is elegant.
One app.
One IP.
One place to patch.
But then you start wanting a little more resilience.
Or a cleaner maintenance story.
Or a way to update one container without making the entire service feel briefly absent.
That is where HAProxy started making sense to me.
Not because a homelab suddenly needs hyperscale theater.
And not because “load balancer” automatically means “serious architecture.”
It became useful because it lets several containers behave more like one deliberate service. And on Proxmox, where spinning up lightweight LXC web nodes is easy, that design starts feeling less like extravagance and more like a clean way to reduce the emotional weight of one container doing everything alone.
- Why multiple web containers sometimes make more sense than one
- What HAProxy is really adding in front of them
- How Proxmox networking makes the pattern easy to build
- Why health checks and persistence matter more than the word “load”
- How I decide whether a homelab app is actually ready for this pattern
HAProxy is not just about scale, it is about steadiness
The HAProxy documentation begins from a place I appreciate: load balancing is about distributing work across resources instead of forcing one node to carry everything alone. That sounds obvious, but in a homelab the more interesting part is not raw scale. It is steadiness.
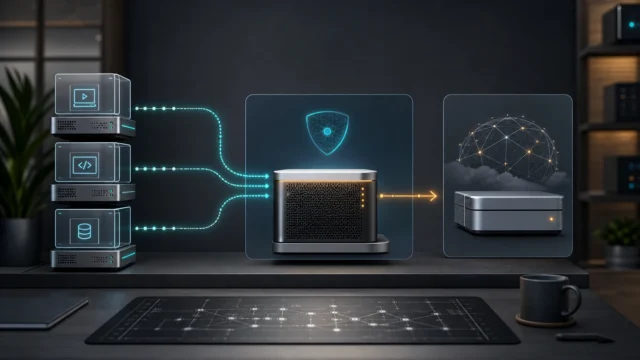
If I place one small HAProxy frontend in front of several web containers, I gain a cleaner entry point for traffic:
- one frontend address or hostname;
- multiple backend containers behind it;
- a place to make routing decisions once instead of everywhere;
- a better maintenance story when one backend needs attention.
That does not automatically make the application highly available in the grand enterprise sense. But it often makes it calmer.
And “calmer” is an underrated design goal in a homelab.
Calmer means I can restart one backend without treating it like a public event.
Calmer means the frontend story remains stable while the backend moves.
Calmer means future changes have a place to live.
That is why I see HAProxy less as a badge of seriousness and more as a tool for architectural composure.
Proxmox makes the container side of this pattern pleasantly straightforward
One reason this design fits Proxmox so well is that Proxmox is already very comfortable with simple, explicit network plumbing. The network documentation makes clear that Proxmox uses the Linux network stack, and the container configuration reference shows that each LXC network interface can be attached to a chosen bridge and can have firewall behavior defined at the interface level.
That matters because it keeps the mental model clean.
You can place:
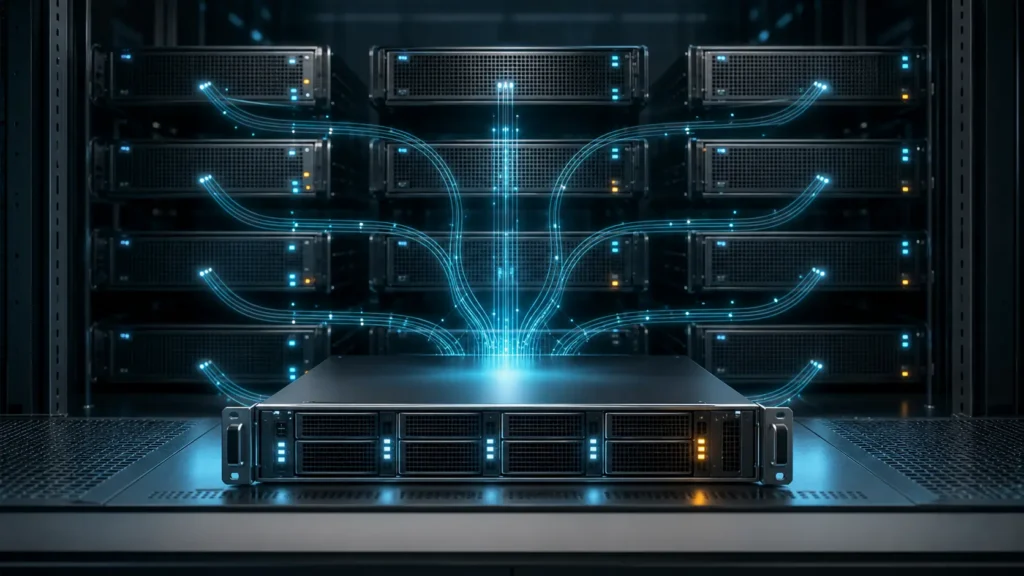
- one HAProxy container at the front;
- two or three web containers behind it;
- all of them on the same bridge, or on a segmented layout if that is the point of the design.
And because Proxmox containers are light, the barrier to trying this is lower than many people expect. If you already like small service-focused LXCs, the pattern feels natural. It pairs especially well with the kind of minimalist container philosophy behind ultra-lightweight homelab services on Alpine LXC.
The architecture stops looking dramatic once you realize it is just:
- a frontend container that speaks for the service;
- several backend containers that actually serve it;
- a bridge or network path that makes their relationship explicit.
That simplicity is a big part of the appeal.
The first mistake is thinking round robin alone solves the whole problem
HAProxy can distribute traffic across backend servers, and the idea of simple round-robin balancing is often where people start. That is fine. In many homelabs, it is also enough for the first version.
But I think this is the point where people become a little too enchanted by the diagram.
Because once you put three web containers behind one frontend, you have not just created “more capacity.”
You have created behavioral questions:
- are the containers identical enough to answer the same way;
- do they share the same content and configuration;
- are sessions or logins sticky in a way the app cares about;
- what happens if one backend is technically alive but functionally unwell.
That is why I do not think the magic word here is load.
I think the magic word is consistency.
If the backend containers do not behave consistently, HAProxy can only distribute inconsistency more efficiently.
So before I celebrate the topology, I want to know whether the app is genuinely fit for several backends. Static sites, simple reverse-proxied apps, and cleanly replicated web services usually behave well. More stateful applications can get complicated fast if they quietly assume one node owns all the context.
Health checks are where the setup starts feeling intelligent
This is where HAProxy becomes more than a traffic splitter.
The official configuration documentation includes health-check behavior such as option httpchk, and this is one of the features that makes the pattern worth doing properly. A backend that merely has a running process is not always healthy in the way a user experiences health.
That difference matters.
I have seen services that:
- accept TCP connections but serve broken responses;
- keep the process alive while the app behind it is half-unwell;
- restart just fast enough to look present and still feel unreliable.
A thoughtful health check gives HAProxy a better idea of which backends deserve traffic.
And in a homelab, that matters even if the traffic volume is small. I am not usually trying to survive a giant spike. I am trying to avoid avoidable fragility. If one container is having a bad day, I would rather the frontend quietly prefer healthier backends than force every client to discover the problem personally.
That is when the setup starts feeling less decorative and more operationally honest.
Persistence matters whenever the app remembers people
This is the second place where homelab enthusiasm can outrun application reality.
Some apps behave beautifully behind a load balancer because each request is basically independent. Others behave politely until someone logs in, uploads something, or opens a longer-lived session that quietly expects continuity.
HAProxy’s documentation includes persistence mechanisms because this is not a rare problem. And in a homelab, I think it is better to acknowledge it early than to call it a surprise later.
If the service behind the frontend depends on per-node session behavior, then you have decisions to make:
- do I want sticky behavior;
- do I want shared session state instead;
- is this even the right app to spread across several containers yet.
This is the part people sometimes skip because the diagram already looked satisfying.
But a balanced architecture that breaks logins, admin panels, or upload flows is not mature.
It is just symmetrical.
HAProxy belongs at the front, but the backend still needs discipline
One thing I like about HAProxy in a Proxmox homelab is that it gives architecture a front door. If I later want TLS termination, cleaner headers, better logging, or a more explicit remote-access story, I now have a defined place where those ideas can live.
That can pair nicely with something like Cloudflare Tunnel in LXC when the goal is to expose a controlled frontend without making every backend node directly important.
But I still think the real work remains behind the proxy.
The backend containers need:
- matching app versions;
- matching content or shared storage where appropriate;
- predictable config;
- a clear understanding of whether local files, sessions, or caches are node-specific.
HAProxy cannot fix backend confusion.
It can only organize traffic around it.
So when this pattern works well, it is usually because the operator was disciplined about the backend first and elegant about the frontend second.
My rule of thumb is to use HAProxy when I want cleaner maintenance, not just more moving parts
This is how I decide whether the pattern is worth it.
If I have one tiny internal app with no availability concern and no real maintenance pain, I probably leave it alone. One container is fine.
If I have a service where I want:
- smoother updates;
- the ability to restart one backend without full user interruption;
- a single clean hostname or entry point;
- a path toward better frontend control;
then HAProxy starts earning its place.
That does not mean I immediately build a miniature production platform.
It just means I stop treating the service as one fragile box and start treating it as a frontend with replaceable workers behind it.
That mental shift is often the real upgrade.
Verification note: Commands, terminology, and support details in this guide were cross-checked against HAProxy’s official configuration tutorials.
For broader context, continue with Docker vs LXC vs Virtual Machines: What Belongs Where in a Homelab? and Managing Container Logs: Preventing Docker from Filling Up Host Disks.
Conclusion
HAProxy on Proxmox is compelling not because it lets a homelab pretend to be a giant platform, but because it gives multiple web containers a cleaner shared frontend and a steadier maintenance story. The official HAProxy documentation gives the core pieces that matter here: backend balancing, health checks, and persistence-aware behavior. Proxmox complements that well because its Linux bridge model and explicit LXC network configuration make it easy to place a frontend container in front of several small web nodes.
What matters most, though, is not the elegance of the diagram. It is whether the backend service is actually ready to behave like one application across several containers. If it is, HAProxy can make the whole stack feel quieter, cleaner, and easier to evolve. If it is not, then all you have done is distribute confusion more evenly. In homelab design, that is an important distinction.
FAQ
Is HAProxy worth using in a homelab if traffic is small?
Yes, if the real goal is cleaner maintenance and a steadier frontend rather than raw scale. Even small traffic can benefit from health-aware backend selection, one stable entry point, and the ability to restart or rotate one container without making the whole service feel like a single fragile node.
Can I just put any web app behind multiple containers and use round robin?
Not safely by default. The app needs to behave consistently across backends, and some services need persistence or shared session state. If the application assumes one node owns the important context, simple balancing can create strange behavior instead of resilience.