People love VPN comparisons that end too quickly.
WireGuard is faster.
OpenVPN is slower.
Case closed.
I understand why that answer became popular. It is tidy, memorable, and often directionally true in the broadest sense. But the more I looked at real firewall and router deployments, the less satisfying that sentence became. It explained the reputation. It did not fully explain the behavior.
What actually matters is not only which protocol name appears in the dropdown. It is how the protocol moves packets, where encryption work happens, how the CPU handles that work, whether the implementation lives mostly in user space or kernel space, whether OpenVPN DCO is present, whether the tunnel is running over UDP or TCP, and whether the hardware itself is strong enough for any of this to matter.
That is why this comparison becomes much more useful once we stop asking, “Which one wins forever?” and start asking, “What kind of overhead is each one creating, and under what conditions does that overhead become visible?”
- Why WireGuard earned its speed reputation so quickly
- Where classic OpenVPN pays extra CPU and packet-handling cost
- Why OpenVPN DCO changes the comparison more than many people realize
- What benchmarks actually measure and what they often hide
- How real-world speed depends on transport, hardware, and policy choices
- When I would still choose one over the other
WireGuard feels fast because its design is trying very hard not to waste motion
This is the cleanest place to start.
WireGuard’s own project site describes it as simple, fast, and modern, and explicitly says it intends to be considerably more performant than OpenVPN. That is not only branding. It reflects real architectural priorities. WireGuard was designed to stay lean, to keep the protocol surface smaller, and to operate in a way that fits naturally into kernel networking on supported systems.
That matters because every layer you remove from the hot path tends to reduce friction.
WireGuard also uses a fixed modern cryptographic suite rather than offering the same breadth of tunable cipher combinations that helped make OpenVPN flexible for many years. In practice, that narrower design often means less negotiation complexity and fewer chances to turn a VPN into a giant compatibility puzzle.
The WireGuard project also notes that ChaCha20-Poly1305 is extremely fast in software on general-purpose CPUs. That point matters for smaller routers and firewalls where raw CPU efficiency is often more important than feature abundance.
This is why WireGuard often feels so good on modest hardware. It is not magic. It is restraint.
Classic OpenVPN carries more overhead because it was built for flexibility first
OpenVPN’s strength has never been minimalism.
Its strength has been adaptability. Authentication options, deployment models, certificates, operating modes, compatibility stories, and the ability to fit difficult real-world requirements gave OpenVPN its long life. That flexibility is valuable. It is also expensive.
In its traditional form, OpenVPN spends more time paying for generality.
OpenVPN historically lives with more userspace involvement in the data path, more context switching, and more room for configuration choices that affect efficiency. That does not mean it is bad. It means its architecture was solving a broader set of problems than “be as lean as possible.”
This is one reason benchmark summaries can mislead people. If you compare classic OpenVPN against WireGuard and stop there, you will often see exactly what the reputation suggests: WireGuard pushes strong throughput with lower CPU cost, while classic OpenVPN burns more cycles to achieve the same job.
That result is real.
It is just no longer the whole story.
OpenVPN DCO changes the conversation because it attacks the overhead directly
This is the part many older mental models miss.
OpenVPN’s current Data Channel Offload documentation says DCO improves performance by moving data-channel processing into the Linux kernel. Netgate’s pfSense documentation explains the same benefit in more operational language: DCO reduces context switching for encrypted OpenVPN data and can provide huge performance gains.
That is not a minor optimization. It is a structural response to the historical reason OpenVPN was often seen as heavier.
In other words, classic OpenVPN and OpenVPN with DCO should not be mentally treated as identical performance categories.
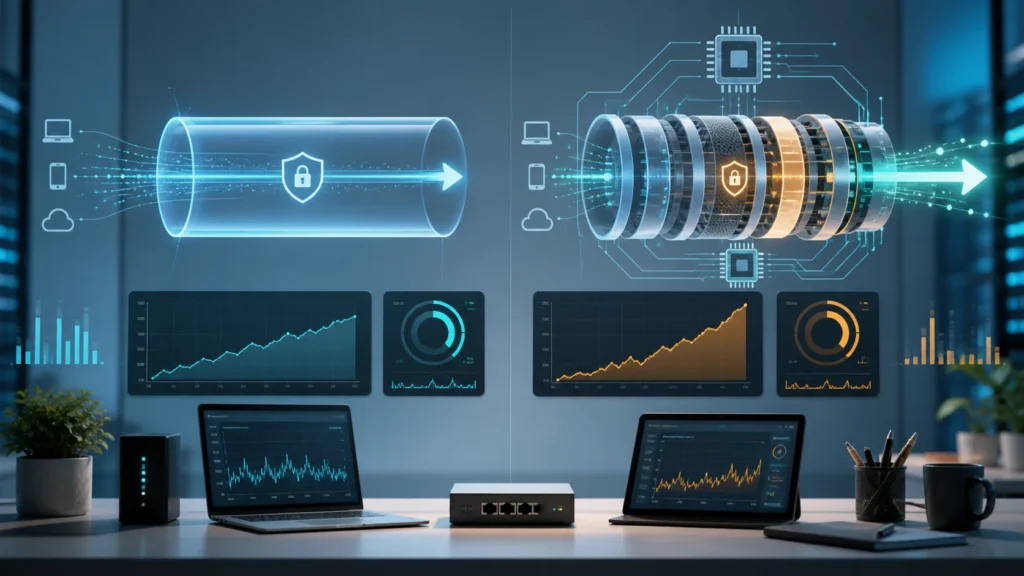
pfSense’s current VPN performance guidance goes even further and says OpenVPN with DCO can, under ideal conditions, match or exceed the performance of WireGuard and IPsec. That sentence deserves careful reading. It is not a promise that OpenVPN always wins. It is a reminder that modern implementation details matter enough to disrupt the old default ranking.
That is why any serious benchmark conversation now needs three buckets, not two:
- WireGuard;
- classic OpenVPN;
- OpenVPN with DCO.
If those are collapsed into a single “OpenVPN” label, the conclusion may be outdated before the test even begins.
Data Channel Offload can change the performance picture dramatically, but only when the environment, platform support, and peer configuration actually allow it to operate as intended.
Benchmarks are useful, but they measure a path, not the whole experience
This is where I think people oversimplify the most.
A benchmark usually captures throughput, CPU load, latency behavior, or some combination of them under a chosen test shape. That is valuable. But it still reflects one route through the maze:
- one hardware platform;
- one MTU reality;
- one transport choice;
- one implementation version;
- one packet size pattern;
- one set of enabled features;
- one kind of background load.
That is why published numbers should be treated as evidence of behavior, not universal prophecy.
If one test says WireGuard reaches line rate more easily on a small appliance, I believe it. If another says OpenVPN with DCO can catch up or surpass it on a different system, I believe that too. Those statements do not contradict each other. They are often just describing different shapes of bottleneck.
The question I care about more is this:
where does the CPU start complaining first?
That is usually the most practical way to think about VPN performance on home-network hardware.
Real-world speed is shaped by more than protocol reputation
This is the part I wish more comparison threads said plainly.
Protocol choice matters, but so do surrounding decisions:
- whether the tunnel uses UDP or TCP;
- whether OpenVPN is using DCO;
- whether the CPU has the right instruction support and enough headroom;
- whether the firewall is also doing IDS, QoS, shaping, or heavy inter-VLAN filtering;
- whether the remote side is weaker than the local side;
- whether the traffic pattern is many small flows or one big transfer.
Even transport details matter a lot. pfSense’s documentation notes that OpenVPN over TCP is likely to reduce VPN performance compared with the more typical UDP approach. That is not just a tuning footnote. It is one reason “OpenVPN felt slow for me” may describe a deployment choice as much as a protocol truth.
This is also where practical network design comes back into the picture. If the same appliance is handling VLAN boundaries, DHCP logic, firewall policy, DNS decisions, and VPN encryption all at once, the CPU story becomes part of the architecture story. That is one reason performance conversations connect naturally to things like VLAN planning and even to how I think about firewall platforms in choosing OPNsense for home use. The VPN does not run in isolation. It competes with everything else the box is already doing.
So which one feels faster in practice?
If I had to say it plainly, I would say this:
WireGuard usually wins the simplicity-to-speed ratio.
It often reaches strong real-world performance with lower fuss, lower apparent CPU overhead, and less configuration complexity, especially on small routers and firewalls. If someone wants efficient site-to-site links or fast remote access without needing OpenVPN’s broader compatibility story, WireGuard often feels like the cleaner answer.
Classic OpenVPN usually feels heavier.
That does not mean it is obsolete. It means you should expect more overhead unless there is a reason its feature set, compatibility, or operational model matters enough to justify it.
OpenVPN with DCO is the category that forces humility.
Once DCO enters the picture, older assumptions can become unreliable. The gap can narrow sharply, and in some environments OpenVPN’s reputation for being the obviously slower option stops being accurate enough to trust casually.
That is the real conclusion I have landed on.
Not “WireGuard always wins.”
Not “OpenVPN is still secretly faster.”
But rather:
architecture decides how honest the benchmark feels.
Verification note: Commands, terminology, and support details in this guide were cross-checked against WireGuard’s official performance documentation and the official OpenVPN 2.6 manual.
For broader context, continue with The Anatomy of an IP Address: Public vs. Private Ranges Explained and Why I Chose OPNsense for My Home Network.
Conclusion
WireGuard vs. OpenVPN is no longer a comparison between one obviously modern option and one permanently slower legacy choice. The older reputation still points in a useful direction: WireGuard is lean, efficient, and often easier on CPU overhead, while classic OpenVPN usually pays more for its flexibility. But OpenVPN with DCO changes that landscape enough that serious comparisons now need more precision than old one-line answers allow.
That is why I think the best takeaway is not a slogan. It is a testing mindset. Ask where the work happens, how many context switches the system is paying for, whether kernel offload is in play, whether the tunnel is using UDP cleanly, and which box in the path runs out of CPU first. Once you look at those things, the benchmark numbers stop feeling mysterious and start feeling explainable.
FAQ
Is WireGuard always faster than OpenVPN?
Not always. WireGuard often has the cleaner performance profile, especially against classic OpenVPN, but OpenVPN with Data Channel Offload can narrow the gap substantially and may match or exceed WireGuard in some environments.
Why does OpenVPN traditionally use more CPU?
Because its traditional architecture carries more userspace overhead, more context switching, and more flexibility-related complexity in the data path than WireGuard’s leaner approach.
What does OpenVPN DCO actually improve?
It moves OpenVPN data-channel processing into the Linux kernel, which reduces context switching and can improve throughput, latency behavior, and CPU efficiency under load.
Why do benchmark numbers vary so much from one comparison to another?
Because VPN performance depends heavily on hardware, transport, packet sizes, enabled features, background load, and implementation details. Published benchmark numbers describe a tested environment, not every environment.
Should I still choose OpenVPN if WireGuard is simpler?
Sometimes yes. OpenVPN may still be the better fit when you need its compatibility, authentication ecosystem, deployment familiarity, or feature set. The right choice is not only about peak speed.